Artificial intelligence is changing how banks detect fraud, assess credit risk, support customers, and manage cybersecurity. However, as financial institutions adopt increasingly advanced AI systems, regulators are paying closer attention to the risks these technologies may create. Recent IT industry news highlights growing concern among US banking watchdogs about the potential impact of AI on financial stability.
According to a Reuters report published on October 13, 2026, US banking regulators are increasing their scrutiny of how banks use AI, including autonomous AI agents in cybersecurity and risk management. The review involves agencies such as the Federal Reserve, the Federal Deposit Insurance Corporation, and the Office of the Comptroller of the Currency.
This development reflects a broader shift in financial services. While AI can improve efficiency and decision making, its growing role in critical operations raises questions about accountability, transparency, and operational resilience.
Why AI Adoption Raises Financial Stability Concerns
Banks operate within a highly interconnected financial ecosystem. A technology failure at one institution can affect customers, business partners, and other financial organizations. Consequently, regulators want to understand whether AI systems could introduce risks that traditional controls are not equipped to manage.
For example, an AI model used to assess lending applications could produce unreliable results if its training data is incomplete or biased. Similarly, an automated system responsible for detecting suspicious transactions might overlook emerging fraud patterns or incorrectly flag legitimate payments.
Autonomous AI agents introduce additional complexity because they can perform tasks and make decisions with limited human intervention. If these systems have excessive permissions, weak safeguards, or inadequate monitoring, a technical error could quickly become a serious operational problem.
These concerns are increasingly central to finance industry updates, particularly as institutions move from experimental AI projects to systems that influence essential business functions.
Cybersecurity and Human Oversight Take Priority
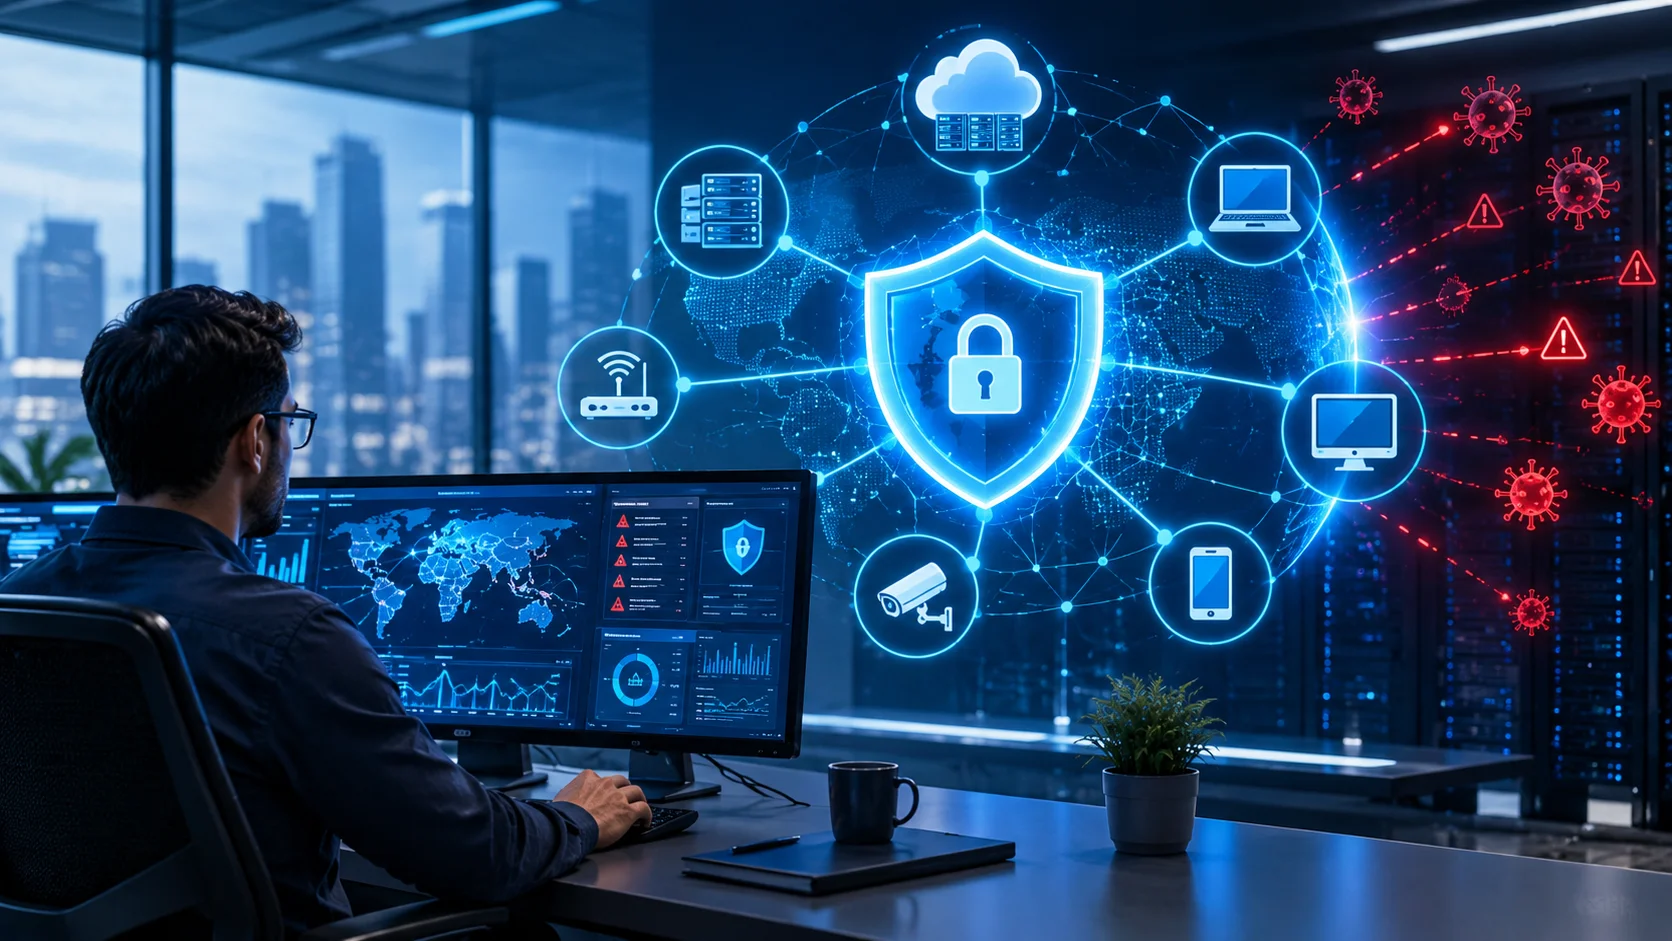
Cybersecurity is a major focus of the growing regulatory attention. Banks face persistent threats from phishing, ransomware, identity theft, and increasingly sophisticated automated attacks. AI can strengthen threat detection by analyzing large volumes of activity and identifying unusual patterns. Nevertheless, attackers can also exploit AI to improve their techniques.
Therefore, financial institutions need security controls that address both the benefits and limitations of AI. These include access restrictions, regular model testing, audit trails, incident response procedures, and clear processes for disabling systems that behave unexpectedly.
Human oversight is equally important. AI should not automatically become the final authority for every high impact decision. Instead, banks need to determine which activities can be automated safely and which require review by qualified employees.
Moreover, employees must understand when AI recommendations are unreliable and how to report problems. This makes training and accountability important parts of digital transformation, rather than technical tasks that can be handled by IT departments alone.
What Increased AI Scrutiny Means for Banking Technology
Regulatory attention does not necessarily mean banks must slow innovation. Instead, it encourages financial institutions to build dependable technology systems before deploying AI at scale.
Banks may need to strengthen their model governance practices, document how automated decisions are made, and test systems under realistic failure scenarios. They should also assess third party technology providers because dependence on a small number of AI platforms can create operational concentration risks.
For technology leaders, the challenge is to connect innovation with reliable controls. AI governance should involve cybersecurity specialists, compliance teams, risk managers, business leaders, and software engineers from the beginning of a project.
Additionally, institutions should establish clear ownership for every AI application. Teams need to know who approves deployment, who monitors performance, and who responds when the system produces harmful or unexpected results. These technology insights are relevant beyond banking, particularly for businesses introducing automation into essential workflows.
The increasing scrutiny of AI in banking could influence how other industries manage intelligent automation. Healthcare providers, insurance companies, technology businesses, and large retailers also rely on systems that process sensitive information or support important decisions.
For example, HR trends and insights increasingly involve AI powered recruitment and workforce planning tools. Sales strategies and research may use predictive models to prioritize leads, while marketing trends analysis often relies on automated personalization and customer segmentation. In each case, organizations must balance efficiency with privacy, fairness, and human accountability.
Banking regulation can therefore provide useful lessons for the wider IT ecosystem. Businesses should understand what their AI systems can access, test how they behave under unusual conditions, and maintain human review for decisions with significant consequences.
However, regulatory requirements differ by industry and jurisdiction. Companies should assess the rules that apply to their own operations instead of assuming that every banking requirement applies to all AI users.
Preparing for the Next Phase of AI Governance
As regulators examine AI adoption more closely, financial institutions should treat governance as an ongoing operational responsibility. Effective oversight requires regular risk assessments, documented controls, employee training, vendor reviews, and clear procedures for investigating incidents.
Banks should also evaluate whether their existing recovery plans account for AI related failures. Traditional business continuity measures may not fully address corrupted model outputs, compromised AI agents, or unexpected interactions between automated systems.
Meanwhile, technology teams should measure AI performance beyond speed and cost savings. Reliability, explainability, security, and the ability to recover from failures are equally important indicators of success.
The direction of future oversight will depend on regulatory findings and how quickly AI capabilities evolve. Nevertheless, organizations that establish strong safeguards now will be better positioned to innovate responsibly and respond to changing expectations. As this story continues to shape IT industry news, the key lesson is that trustworthy AI depends not only on advanced technology but also on sound governance and accountable human decisions.
Explore more Technology insights and the latest IT industry news at iTechInfoPro.com.
Visit iTechInfoPro.com for expert perspectives on digital transformation, cybersecurity, and emerging technology trends.
Source : reuters.com